IT/OT Convergence: Bridging Operations and Security
What changes, technically and organizationally, when industrial networks meet IT-grade security. We look at segmentation, legacy protocol risks, and the change-management hurdles that trip up otherwise solid projects.
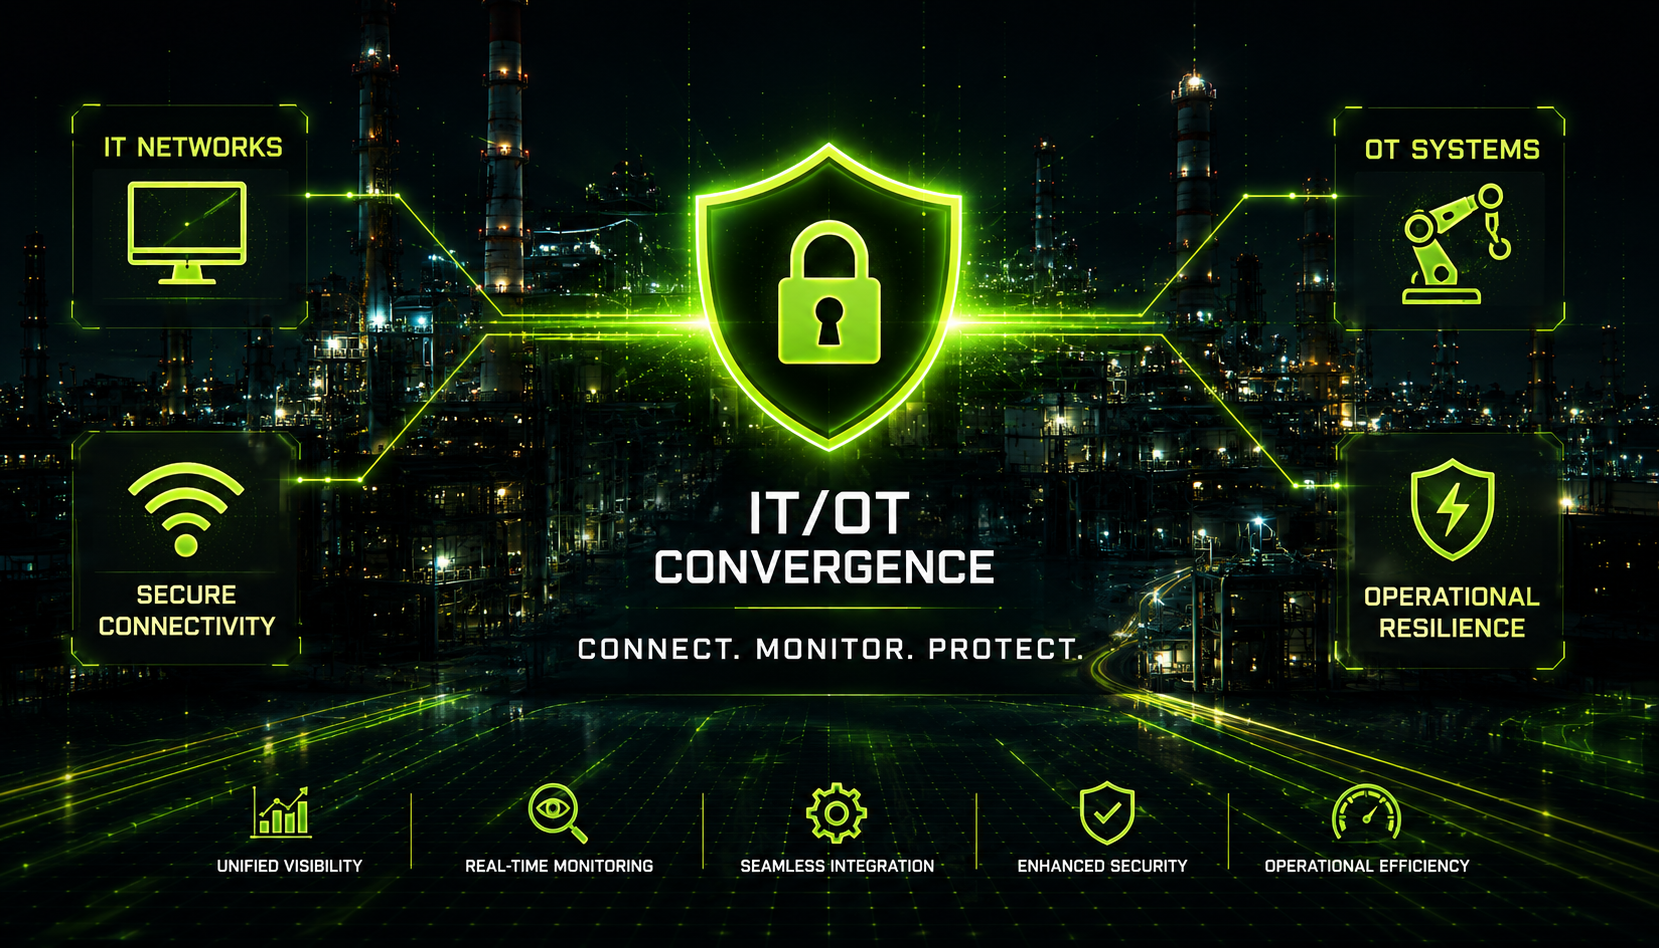
When Industrial Controls Meet IT-Grade Security
For decades, Operational Technology (OT) networks ran in complete isolation from corporate IT networks. Industrial Control Systems (ICS), SCADA platforms, and PLCs were designed for physical reliability and uptime rather than cyber defense. Today, Industry 4.0 initiatives demand real-time data flow between plant floors and cloud analytics, blurring traditional air-gaps.
Merging enterprise IT networks with physical OT environments introduces unprecedented operational efficiency, but it also opens critical industrial infrastructure to modern web-borne cyber threats.
Why IT/OT Integration Projects Fail
Applying standard IT security policies directly to industrial floors often causes unplanned downtime, broken legacy protocols, and cultural friction.
Legacy Protocol Vulnerabilities
Industrial protocols like Modbus, DNP3, and PROFINET were built without encryption or authentication, making them vulnerable to packet injection once breached.
IT vs. OT Cultural Silos
IT prioritizes data confidentiality and rapid patching, while OT prioritizes safety, physical availability, and zero production interruptions.
Successful convergence requires custom architecture, specialized OT visibility tools, and unified governance across both engineering and security teams.
6 Pillar Strategies for Secure IT/OT Convergence
Network Micro-Segmentation
Implement strict Purdue Model zone segmentation using industrial firewalls to isolate enterprise networks from critical ICS controls.
Passive Asset Discovery
Deploy passive network monitoring tools to map connected OT assets and baseline normal communications without interrupting sensitive PLCs.
Zero Trust Remote Access
Replace legacy VPNs with granular Zero Trust Network Access (ZTNA) and session recording for third-party vendor maintenance.
OT-Aware Vulnerability Management
Establish risk-based patching workflows tailored to scheduled maintenance windows, replacing disruptive auto-updates.
Unified Cross-Departmental Teams
Bridge organizational friction by building joint IT/OT security steering committees and cross-training engineering personnel.
Centralized Threat Monitoring
Feed OT protocol logs and anomaly alerts into a centralized 24/7 Security Operations Center (SOC) for real-time threat detection.
Securing Critical Infrastructure with Maroev
Maroev delivers comprehensive IT/OT network engineering and cybersecurity solutions tailored for manufacturing, energy, and utility sectors across the Philippines. We understand the delicate balance between physical operational uptime and robust digital defense.
From passive protocol inspection to industrial firewall architecture, Maroev ensures your smart factory or utility grid operates safely, securely, and without interruption. Explore our capabilities on our ICT & cybersecurity solutions page.
Phased Plan for IT/OT Security Integration
Secure convergence is a continuous journey. Follow these essential stages to transform your industrial operations.
Conduct a passive asset audit to discover all connected PLCs, HMIs, and OT network pathways.
Enforce DMZ boundaries and Purdue Model network segmentation between IT and OT domains.
Implement multi-factor authentication (MFA) and ZTNA for all remote engineer and vendor accesses.
Integrate industrial security event telemetry into a unified 24/7 SOC for continuous threat monitoring.
Maroev works alongside your site engineers to design, build, and maintain secure industrial network architectures without impacting productivity.
Safeguard Your Industrial Operations Today
Unify your operational efficiency and cybersecurity resilience without risking uptime. Partner with Maroev to build secure, segmented, and fully monitored IT/OT environments.
Book a Consultation →