Building a Resilient SOC for the Philippines
Lessons from real-time monitoring and proactive defense. From visualizing threats to scaling automated incident response, we cover the controls that matter most for teams striving to achieve digital sovereignty. As regional data risks grow, learn how to build a security operations center that doesn’t just survive, but thrives.
Addressing the Regional Threat Volume Surge
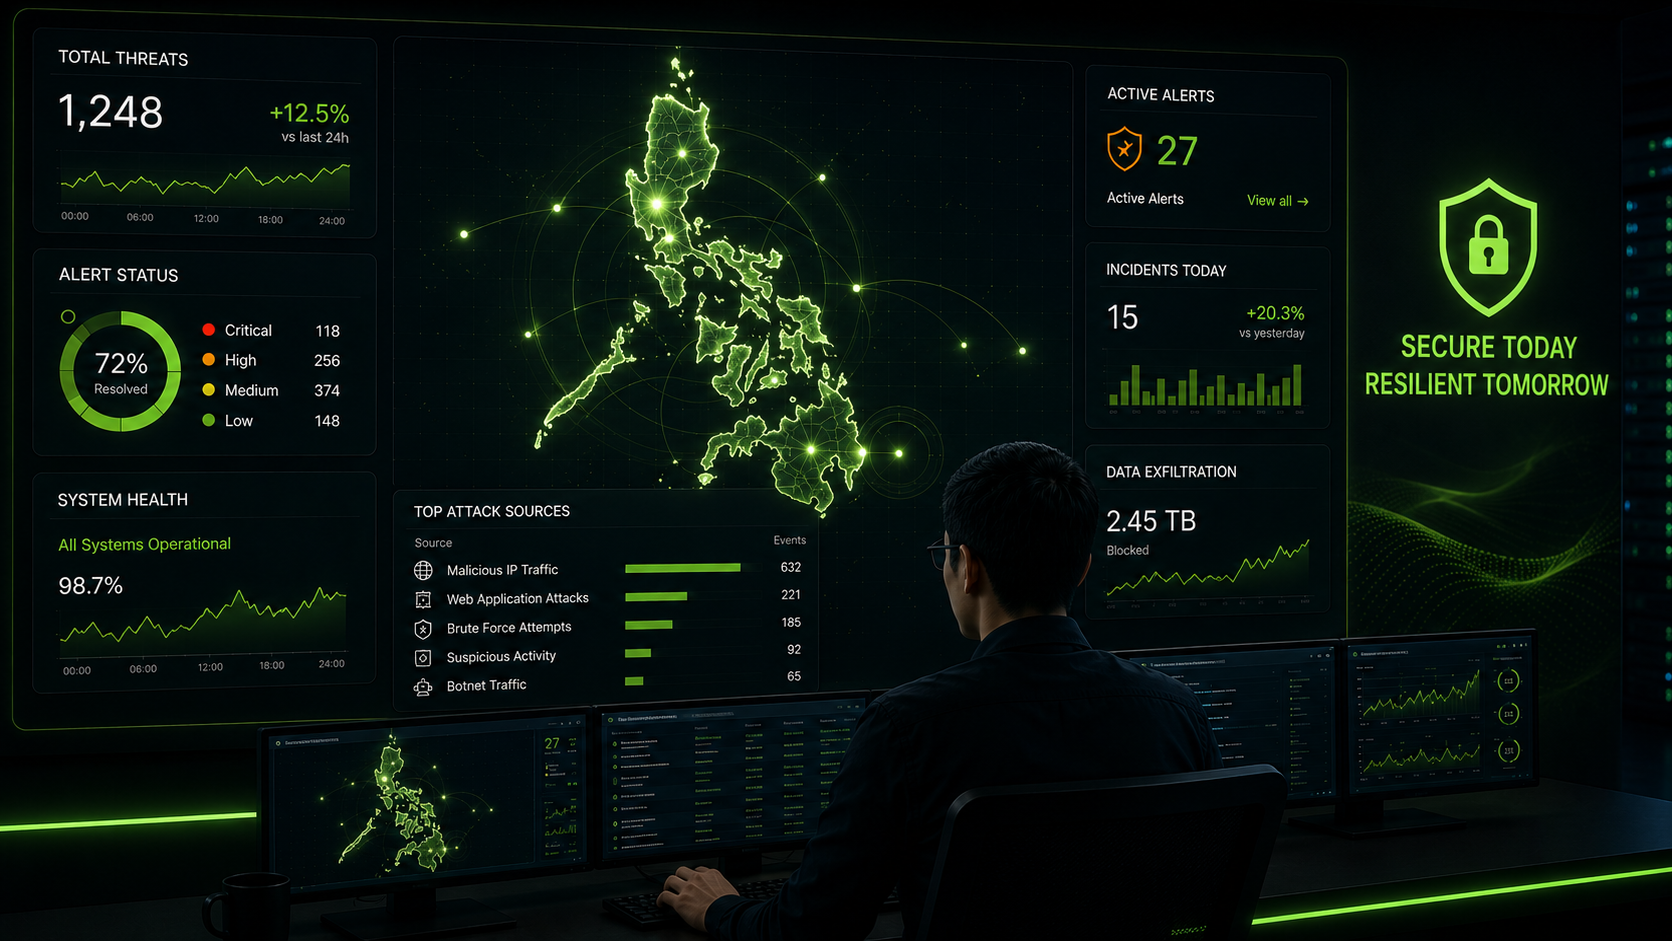
Philippine enterprises face an evolving wave of targeted cyber threats, marked by a 12.5% increase in total threat activity over short windows. Relying on legacy perimeter defenses is no longer sufficient when facing high-density attack vectors aimed directly at local critical infrastructure.
By shifting toward continuous threat telemetry and localized threat intelligence, security operations centers can track malicious activity down to specific geographical origin points across the archipelago in real time.
Primary Vectors Facing Modern Enterprise SOCs
Understanding high-frequency intrusion patterns allows security teams to optimize ingestion filters and defense priorities.
Malicious IP Traffic & Web Attacks
Continuous scanning from infected botnets and targeted web application attacks constantly probe enterprise edge routers and public endpoints for unpatched vulnerabilities.
Brute Force & Credential Abuse
Automated password spraying and credential stuffing attempts repeatedly bombard authentication gateways to establish unauthorized initial access.
A localized SOC architecture correlates these raw events immediately, distinguishing noise from legitimate high-severity breaches.
5 Key Metrics a Resilient SOC Tracks
Total Threat Telemetry
Aggregates global and regional threat signals to identify sudden surges in inbound malicious traffic before networks saturate.
Active Alert Categorization
Classifies incidents by severity—Critical, High, Medium, and Low—ensuring tier-1 analysts address immediate risks first.
Data Exfiltration Prevention
Monitors outbound payload volumes in real time, stopping terabytes of unauthorized data transfers before sensitive files escape.
System Health & Operational Uptime
Tracks continuous operational readiness (target 98.7%+) across all monitored cloud connectors, servers, and security appliances.
Automated Alert Resolution Rate
Measures the percentage of routine alerts resolved through automated playbooks (e.g., 72%+ target), drastically lowering analyst fatigue.
Building Sovereign Digital Resilience
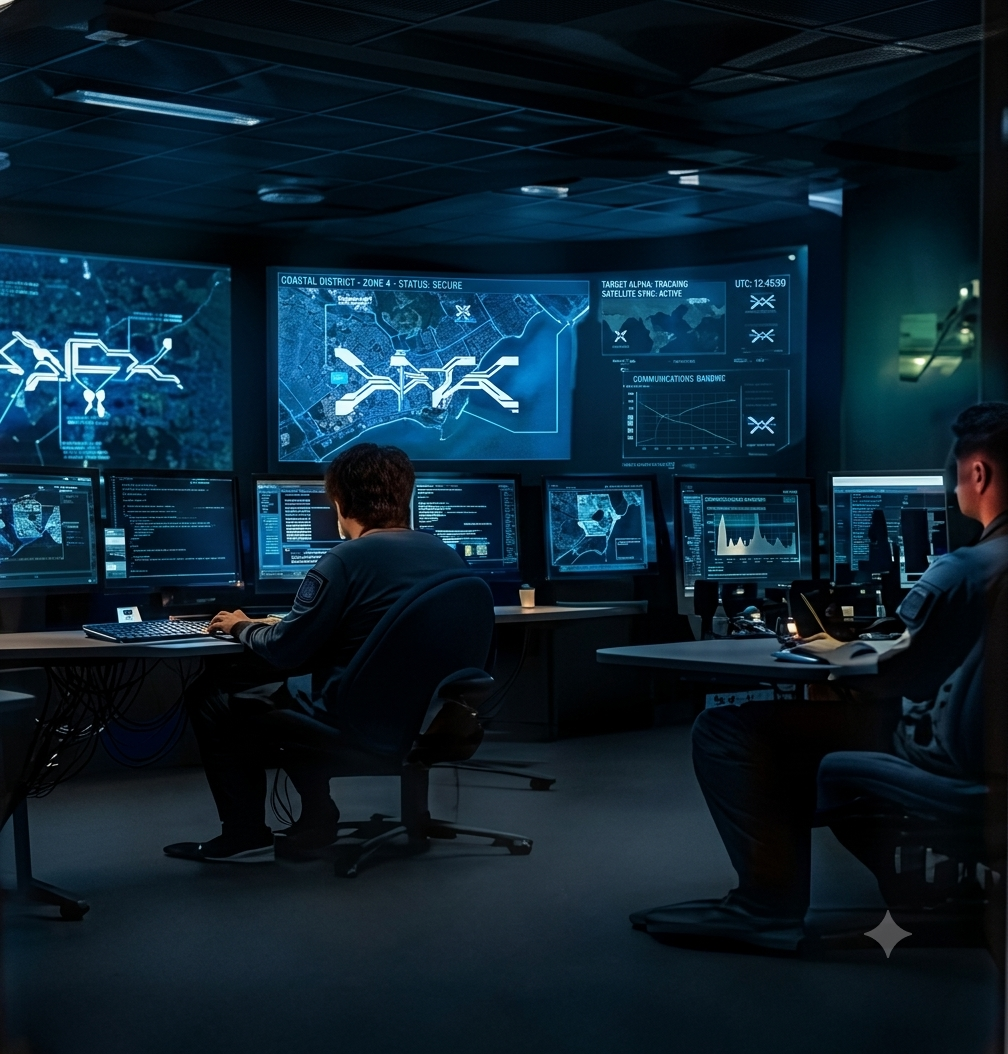
Maroev’s Security Operations Center blends advanced automation with local threat context tailored specifically for organizations operating in the Philippines. By visualizing regional attack maps and pairing real-time SIEM analytics with immediate triage, we transform raw data into proactive defense.
Our approach ensures your security operations don’t just passively alert you to incidents, but execute rapid containment actions to secure critical systems. Learn more about our continuous defense strategies on our cybersecurity solutions page.
Steps to Achieving SOC Resilience
Building a high-performing security center requires clear operational integration and real-time visibility. Follow these steps to fortify your operations.
Establish continuous ingestion across all regional networks, endpoints, and cloud infrastructure.
Deploy localized threat intelligence feeds to identify attack vectors targeting domestic industries.
Implement SOAR automation playbooks to instantly block malicious IP traffic and halt data exfiltration.
Maintain continuous 24/7 human oversight to triage high-priority critical alerts and perform proactive threat hunting.
Maroev works with regional organizations to assess, build, and manage SOC capabilities designed for sustainable, long-term resilience.
Secure Today, Resilient Tomorrow
Don’t leave your enterprise vulnerable to evolving regional threat vectors. Partner with Maroev to build a modern SOC that delivers real-time visibility, automated incident response, and long-term digital sovereignty.
Book a Consultation →