Choosing the Right MFA: A Buyer’s Guide
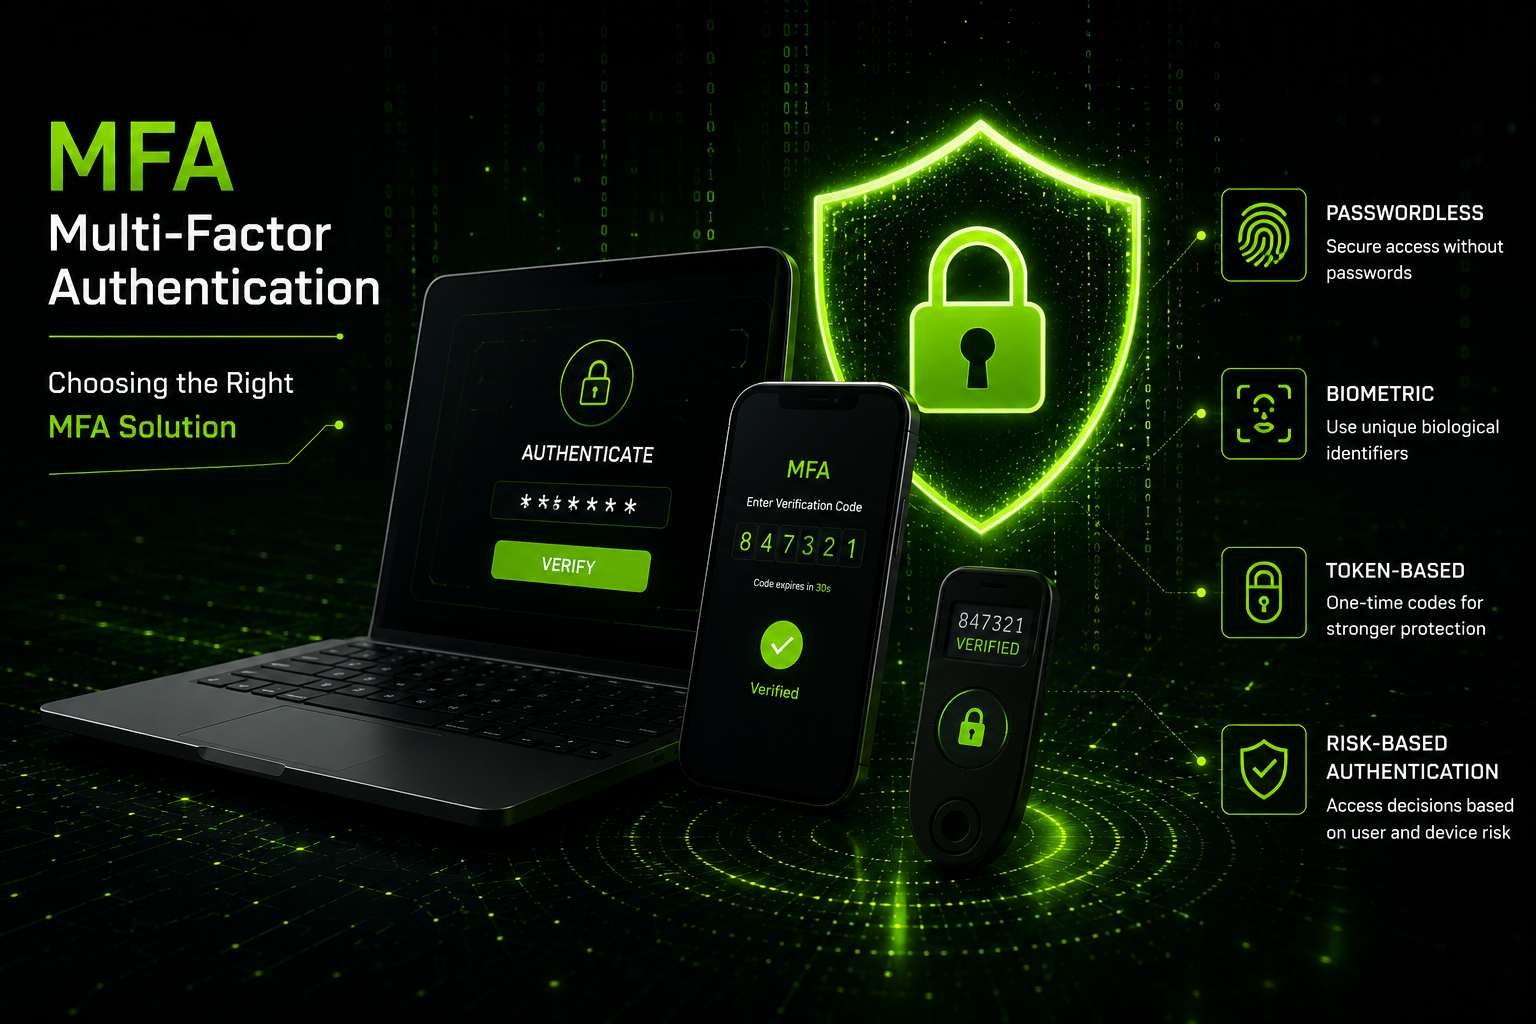
Passwordless, biometric, or token-based: how to pick an authentication model that fits your risk profile. We compare rollout cost, user friction, and phishing resistance across the most common MFA approaches available today.
Beyond Simple Passwords: Modern Authentication
With over 80% of data breaches tracing back to stolen or compromised credentials, Multi-Factor Authentication (MFA) is no longer optional—it is the foundational gatekeeper of enterprise security. However, not all MFA methods offer equal protection.
From SMS OTPs to FIDO2 WebAuthn security keys, selecting the wrong MFA strategy can either leave critical vulnerabilities open to adversaries or paralyze user productivity with excessive friction.
MFA Authentication Models Evaluated
Balance security posture against deployment complexity and end-user adoption barriers.
SMS & Voice OTP
Delivers basic security via text message. Highly vulnerable to SIM swapping, SS7 interception, and phishing attacks.
TOTP Authenticator Apps
Time-based 6-digit codes generated via apps like Google or Microsoft Authenticator. Immune to SIM swaps, but vulnerable to adversary-in-the-middle phishing.
Push Notifications & Biometrics
One-tap mobile approvals with biometric verification (Face ID/Fingerprint). Highly convenient, though require number-matching to prevent MFA fatigue attacks.
FIDO2 / WebAuthn Hardware Tokens
Physical security keys (e.g., YubiKeys) and device-bound passkeys. Completely immune to man-in-the-middle phishing, providing enterprise-grade defense.
4 Key Pillars for Evaluating an MFA Solution
Phishing Resistance
Ensure the authentication mechanism cryptographically binds the login session to the domain, rendering credential harvesting useless.
User Experience & Friction
Minimize user pushback by selecting passive or seamless biometric options that streamline login speeds without sacrificing safety.
Identity Ecosystem Compatibility
Verify full compatibility with your primary Identity Providers (IdP) such as Microsoft Entra ID, Okta, Ping Identity, or legacy Active Directory.
TCO & Operational Overhead
Account for ongoing hardware costs, token distribution logistics, and self-service account recovery workflows to keep helpdesk ticket costs down.
Architecting Phishing-Resistant Identity Security
At Maroev, we evaluate your organization’s risk profile, regulatory compliance needs, and current infrastructure to design and deploy seamless Multi-Factor Authentication strategies across the Philippines.
Whether you need FIDO2 hardware token rollouts for operational teams or adaptive context-aware access for remote workforces, Maroev balances security with seamless user experience. Learn more about our specialized IAM services on our cybersecurity solutions page.
Phased MFA Implementation Process
Deploying authentication controls without disruption requires a structured, step-by-step approach.
Perform identity risk assessments and group users into specific access tiers (e.g., Privileged Admins, Remote Users, On-site Personnel).
Select appropriate MFA authenticators per risk tier and enforce adaptive risk-based conditional access policies.
Establish automated self-service registration and robust identity verification recovery channels.
Execute phased pilot rollouts followed by organization-wide enforcement and continuous monitoring.
Ready to Secure Your Workforce Identity?
Eliminate credential vulnerabilities with tailored, phishing-resistant Multi-Factor Authentication. Partner with Maroev to build a resilient, frictionless authentication framework.
Schedule an Assessment →