Why Your Organization Needs a 24/7 SOC
The operational benefits of round-the-clock threat detection and intelligence. Discover how real-time telemetry, automated triage, and proactive threat hunting protect critical infrastructure from after-hours attacks.
Cyber Threats Don’t Work 9-to-5
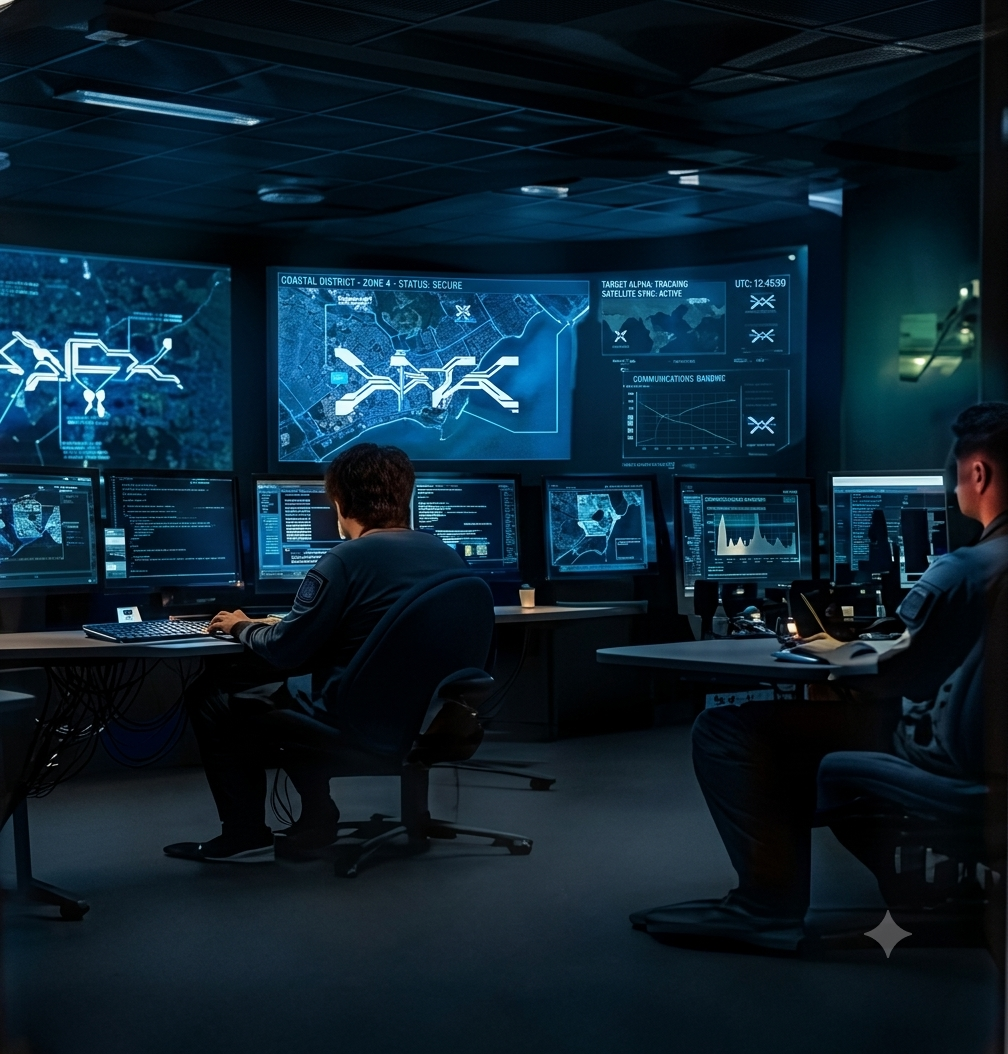
A 24/7 Security Operations Center (SOC) serves as your organization’s centralized command post for real-time monitoring, incident response, and continuous threat mitigation. Attackers frequently exploit weekends, holidays, and off-hours to launch ransomware and breach networks when internal IT teams are offline.
A modern SOC transitions your defense strategy from reactive disaster management to proactive, continuous containment.
Why Traditional Business-Hours Security Leaves You Vulnerable
Relying solely on standard business hours leaves a massive security blind spot that attackers actively look to exploit.
After-Hours Exploitation
More than 70% of ransomware attacks occur after hours or on weekends when response times are slowest, letting threat actors move laterally unchecked.
Alert Fatigue & Misdirection
In-house security teams are inundated with thousands of daily alerts, leading to missed high-severity threats without dedicated 24/7 triage analysts.
By the time your IT team logs in on Monday morning, an uncontained breach can result in complete network encryption, stolen intellectual property, and devastating downtime.
5 Key Operational Benefits of a 24/7 SOC
Real-Time Telemetry & Monitoring
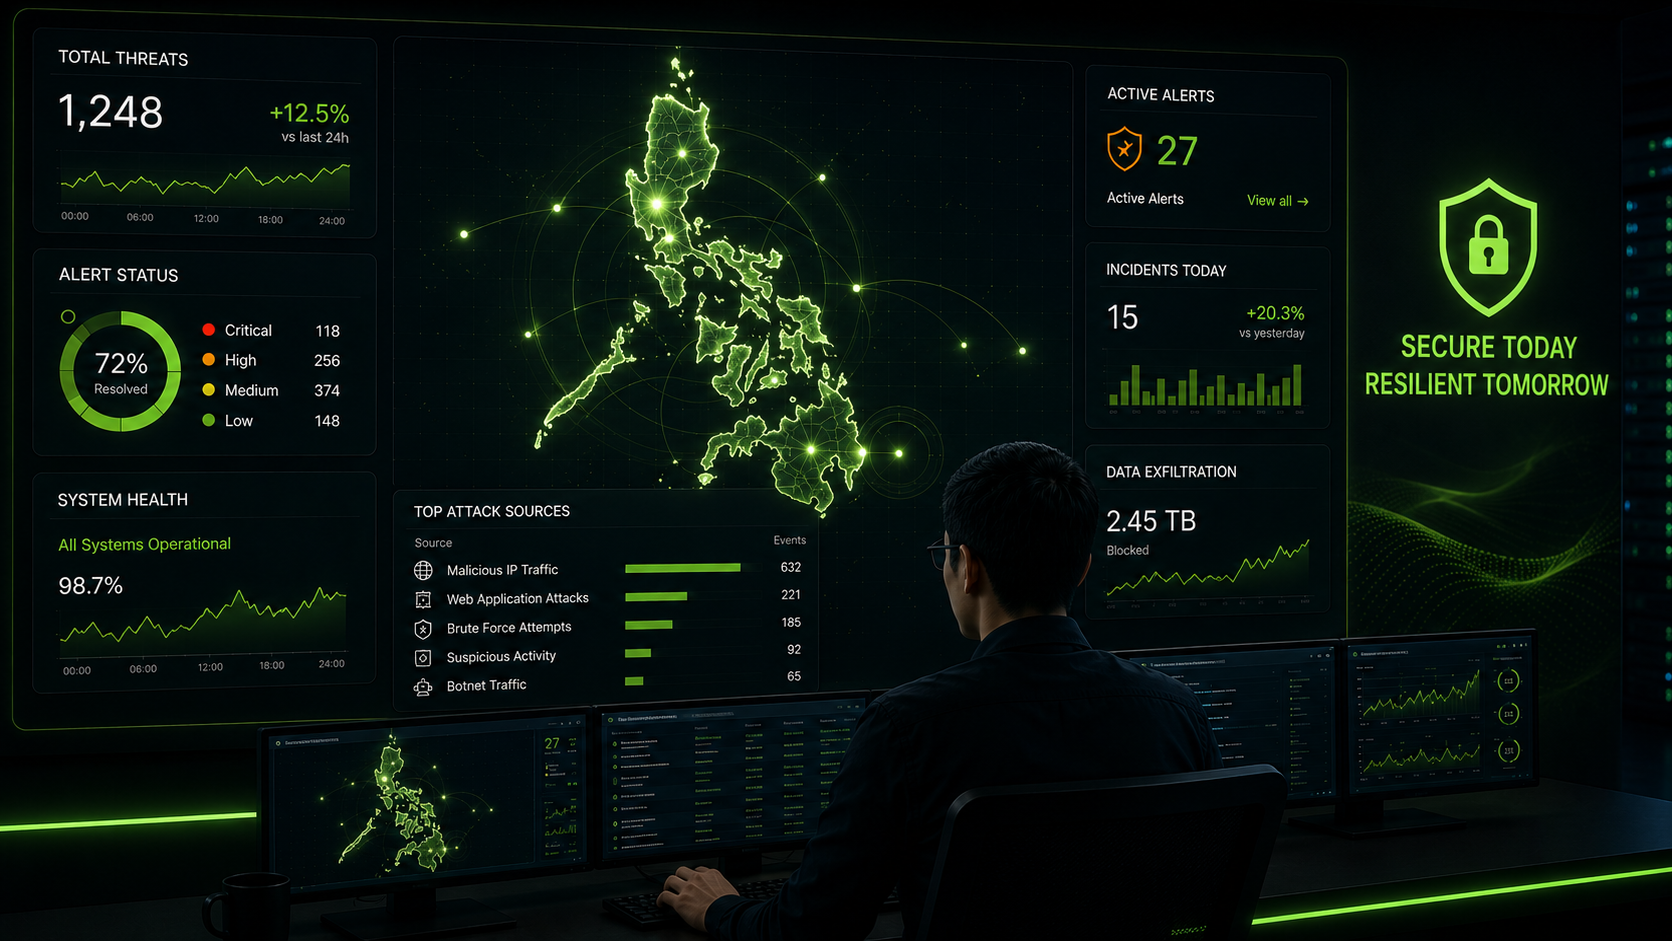
Continuous ingestion and correlation of log data across endpoints, cloud workloads, and networks ensure complete environment visibility.
Automated Triage & Filtering
AI-driven SIEM and SOAR integrations eliminate noise, filtering out false positives so analysts focus exclusively on genuine security incidents.
Proactive Threat Hunting
Expert security analysts continuously hunt for hidden compromise indicators (IOCs) and evasive malware that bypass traditional firewalls.
Rapid Containment & Remediation
Automated playbooks isolate compromised hosts and revoke compromised credentials in seconds, curtailing damage immediately.
Continuous Regulatory Compliance
Meets strict logging and monitoring requirements for regulatory standards like ISO 27001, PCI-DSS, and local data privacy laws.
How Maroev’s Next-Gen SOC Protects Your Enterprise
At Maroev, our Managed SOC operations combine cutting-edge SIEM, XDR, and SOAR technologies with experienced threat analysts to deliver round-the-clock defense tailored to enterprise environments.
Rather than overburdening your internal resources, Maroev acts as an extension of your team—providing actionable threat intelligence, rapid incident containment, and seamless escalation without the expense of building an in-house 24/7 facility. Discover more on our cybersecurity solutions page.
Steps to Building SOC Readiness
Transitioning to a 24/7 security monitoring model doesn’t require an overnight complete overhaul. Follow a structured path to integrate managed SOC capabilities smoothly.
Audit current logging, network telemetry, and endpoint coverage across all enterprise assets.
Establish clear incident escalation protocols and automated containment playbooks.
Integrate core data sources into centralized SIEM/XDR platforms for unified visibility.
Conduct continuous threat-hunting exercises and regular incident response simulations.
Maroev starts every SOC deployment with a comprehensive security posture assessment to identify telemetry gaps and design a customized protection strategy.
Secure Your Enterprise with Round-the-Clock Defense
In today’s cyber landscape, speed is everything. Partnering with a 24/7 Managed SOC ensures that threats are detected, analyzed, and mitigated in real time—protecting your infrastructure, customer trust, and bottom line around the clock.
Book a Consultation →