Cloud Security Best Practices for 2026
Essential steps to keep cloud environments protected as workloads and threats keep evolving. From identity and access management to workload segmentation, we cover the controls that matter most for teams still catching up on cloud posture.
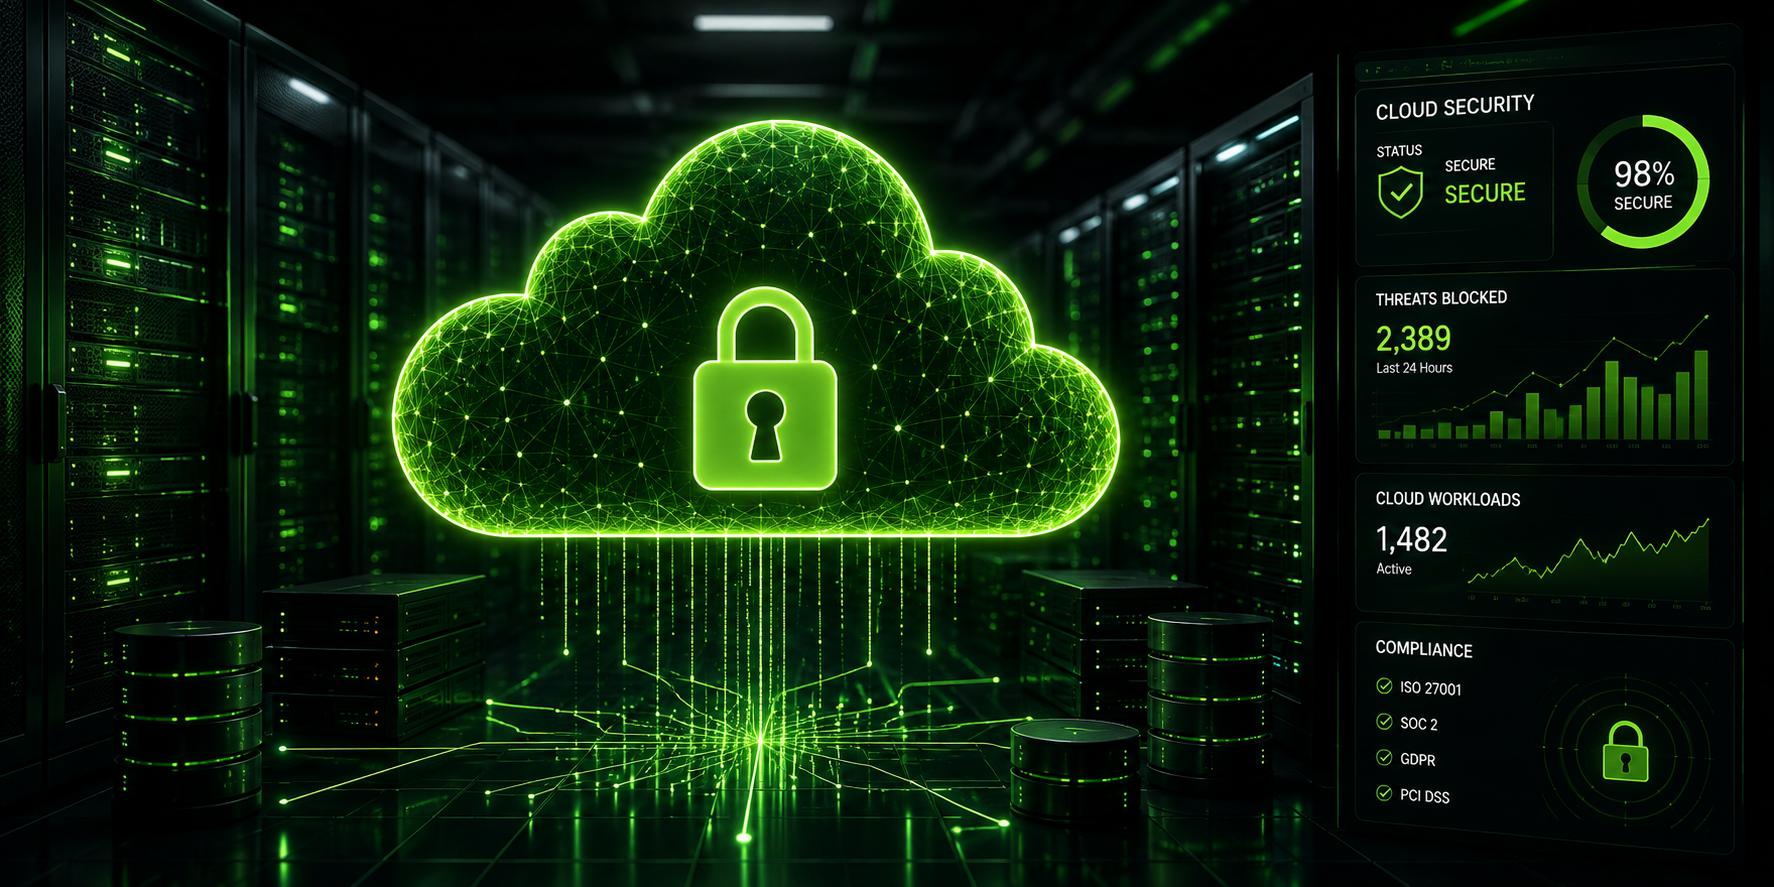
Navigating Complex Cloud Ecosystems in 2026
As enterprise cloud deployments expand across multi-cloud environments like AWS, Azure, and Google Cloud, traditional perimeter defenses continue to lose effectiveness. Misconfigurations, identity over-privileging, and unmonitored API endpoints remain primary attack vectors.
Securing cloud infrastructure requires moving from manual audits to automated, real-time posture governance and proactive threat containment across all cloud workloads.
Key Focus Areas for Modern Cloud Posture
Implement these core governance domains to reduce cloud exposure and prevent credential exploitation.
Cloud Identity & IAM Governance
Enforce strict least-privilege policies, disable long-term access keys, and implement Cloud Infrastructure Entitlement Management (CIEM) to identify over-permissioned human and service accounts.
Automated Misconfiguration Prevention
Utilize Cloud Security Posture Management (CSPM) tools to automatically scan storage buckets, security groups, and API endpoints against CIS benchmarks and compliance frameworks.
Container & Workload Micro-Segmentation
Protect Kubernetes clusters, serverless functions, and virtual machines by isolating east-west traffic and continuously scanning container images for vulnerabilities.
Data Protection & Encryption
Ensure end-to-end encryption for data in transit and at rest using customer-managed keys (CMK), alongside automated data loss prevention (DLP) to classify sensitive stores.
4 Steps to Standardize Your Cloud Defense
Follow this phased checklist to harden your environment against emerging cloud threats.
Centralize Visibility Across Tenants
Gain single-pane-of-glass visibility into all cloud assets, active API gateways, and multi-cloud accounts to eliminate shadow IT resources.
Enforce Zero Trust Access
Mandate phishing-resistant Multi-Factor Authentication (MFA) and conditional access rules for every admin console and Cloud API interaction.
Integrate Security in CI/CD
Scan Infrastructure-as-Code (IaC) templates (Terraform, CloudFormation) during development to catch configuration bugs before deployment.
Continuous SOC & CDR Integration
Feed CloudTrail and cloud audit logs into a unified Security Operations Center (SOC) with Cloud Detection & Response (CDR) capabilities.
Securing Your Cloud Transformation with Maroev
Maroev helps organizations across the Philippines design, implement, and maintain resilient multi-cloud architectures. From CSPM configuration and IAM audits to full SOC monitoring of cloud workloads, we ensure your infrastructure stays compliant and secure.
Explore our full range of cloud governance and cyber defense solutions on our ICT solutions provider page.
Harden Your Cloud Environment Today
Speak with our cloud security engineers to perform a cloud posture assessment and eliminate critical misconfiguration risks.
Schedule a Cloud Assessment →